ClickFix Scams Lure Mac and Windows Users into Self-Inflicted Vulnerabilities

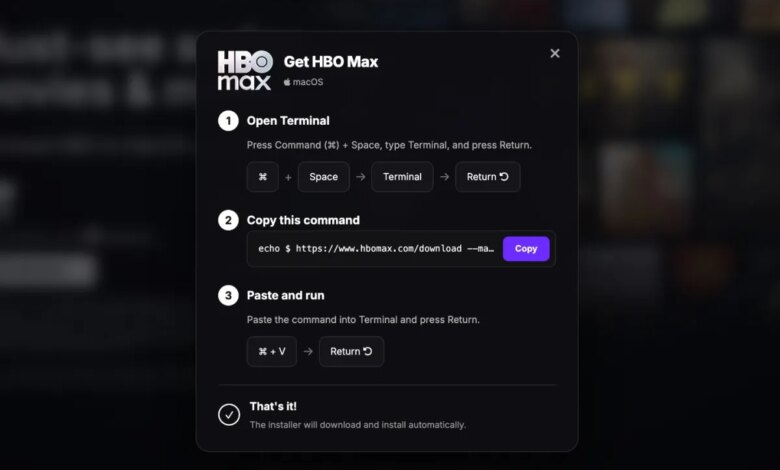
If you recently interacted with an HBO Max advertisement on Reddit, it’s a good idea to scan your computer for potential malware.
These “ClickFix” scams are becoming an increasingly prominent cybersecurity issue in 2026, characterized by their deceptive tactics and increasing prevalence in infecting users’ devices. Initially, these attacks were relatively uncommon, targeting individuals seeking quick tech solutions. However, they have now expanded into a significant global initiative aimed at infiltrating personal computers.
The method involves counterfeit websites or legitimate ones that have been taken over, which present a challenge resembling a CAPTCHA or a bot verification checkbox. When users click on this, they receive instructions prompting them to execute a “check,” which requires copying and pasting specific text into the command prompt for Windows or the Terminal application for Mac.
Once the user presses return, they unknowingly install information-stealing malware on their system, which can immediately harvest their passwords, access their logged-in accounts, and even infiltrate cryptocurrency wallets. Because these attacks utilize the terminal interface, which allows for direct interaction with the operating system via text commands, they frequently bypass antivirus and security systems.
According to cybersecurity researchers, the latest ClickFix scheme involved hackers posting fraudulent ads on Reddit that appeared to promote HBO Max, tricking users into compromising their own systems. The official HBO Max account on Reddit was hacked and used to publish numerous convincing yet fake advertisements, as reported by security experts from Hudson Rock and discussions within Reddit’s cybersecurity community.
It remains uncertain how many individuals clicked on these fake advertisements or were adversely affected. A representative from Warner Brothers Discovery, the parent company of HBO, did not offer any comments upon request.
Reddit acknowledged that it was recently informed of the compromise of an authorized HBO Max account, which was utilized to distribute ads containing harmful links. The account has since been secured, and the ads removed. However, Reddit did not disclose how many users may have interacted with the malicious ads.
While it’s common for software developers to run brief code snippets in the terminal, most everyday users don’t typically use the Command Prompt or PowerShell on Windows, or the Terminal on macOS. Security experts suggest that organizations with multiple Windows machines can restrict access to these features throughout their networks to mitigate the risk of exploitation, according to Kevin Beaumont.
Additionally, as highlighted by Ars Technica, a security tool available for Mac known as BlockBlock can help shield users from attempts to deceive them into compromising their systems.
Article updated with comments from Reddit.