The U.S. Department of Justice is issuing a caution regarding the increasing involvement of North Korean hackers using Americans to execute cyberattacks on U.S. firms.
On Tuesday, federal prosecutors revealed that they have charged and detained at least two individuals, while also executing searches at numerous suspected “laptop farms” in Texas. These facilities were reportedly utilized by North Korean operatives to conduct remote hacks on American companies and to extract confidential information.
The Department of Justice reported that authorities confiscated over 180 computers believed to have been sent by U.S. companies to employees unaware they were hiring North Korean agents posing under stolen identities of American citizens. The DOJ revealed that more than 40 laptop farms across Texas were raided, marking the largest known count of residences being used for North Korean cyber operations, which were linked to at least two American accomplices.
CrowdStrike, which collaborated with the FBI to investigate and disrupt these North Korean activities, stated that these laptop farms are crucial for aiding North Korean hackers in dealing with the challenges of not being physically present in the U.S.
Prosecutors indicated that at least 70 companies based in the U.S. had fallen victim to these hackers, who are estimated to have illicitly acquired around $3 million. Although the DOJ did not disclose the specific companies involved, it noted that they span various sectors including healthcare, cyber support, retail, communications, and manufacturing across Ohio and 16 other states, including the District of Columbia.
“An increasing number of North Korean IT workers are turning to U.S. facilitators to mitigate enhanced detection efforts from the private sector and law enforcement,” stated the Justice Department. “These workers are hiring others to perform a wider range of tasks and, in some cases, are subcontracting entire jobs to foreign nationals.”
North Korean hackers frequently rely on authentic-looking email addresses, impersonated LinkedIn profiles, and extensive online presences to conceal their operations.
In a distinct public service announcement, the FBI noted that there are “thousands” of IT workers under North Korean control employed in Western companies, which create a significant risk to national security and pose threats related to intellectual property theft.
This latest series of arrests and indictments reflects an ongoing effort to combat North Korean activities within the United States. The regime has exploited this “remote IT worker” approach to secure employment with American and European businesses, allowing them to earn salaries while simultaneously stealing sensitive data and intellectual property. Victimized companies then face extortion demands for additional payments from the hackers.
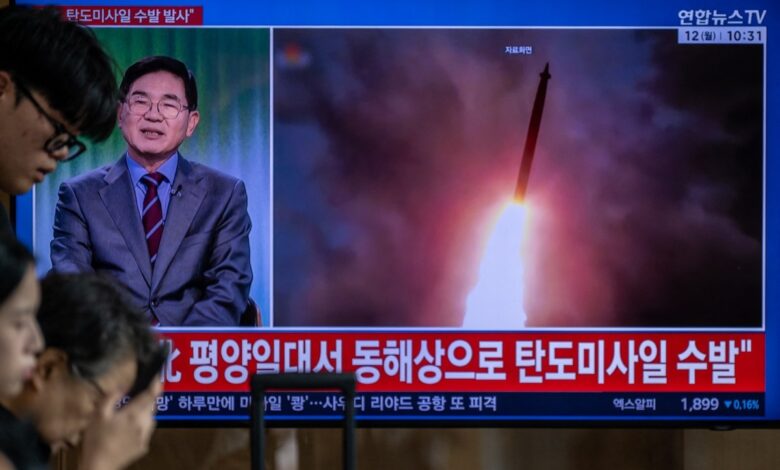
The scheme involving remote IT workers is just one avenue the North Korean regime is pursuing to generate illicit revenue, alongside hacking cryptocurrency exchanges and open-source development projects, aimed at financing its internationally sanctioned nuclear weapons program. It is estimated that the regime has stolen upwards of $2 billion in cryptocurrency in just the year 2025.
Experts on North Korea suggest that the true number of compromised companies and the total stolen cryptocurrency is likely much greater than official reports indicate.
Earlier this year, CrowdStrike reported that North Korean hackers were responsible for around half of all recorded “hands-on-keyboard” cyber intrusions within the past year, referring to attacks executed by human operatives rather than through automated systems or artificial intelligence.