Cyber Intruders Compromise Millions of US Military Personnel Records in Extended Data Security Breach

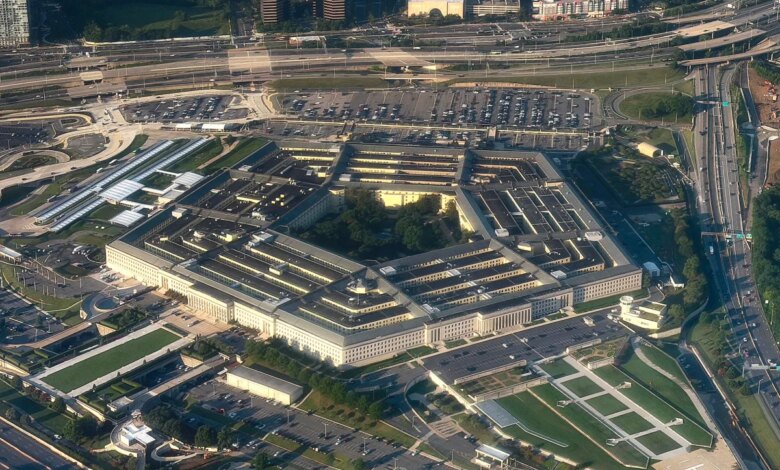
The federal government is notifying millions of present and former U.S. military personnel that their personal details were compromised in a prolonged security incident involving the Pentagon’s personnel database, part of a recent trend of breaches affecting federal employee data.
A notification sent by the Defense Manpower Data Center (DMDC) and circulated on Reddit indicates that several unauthorized individuals took advantage of a vulnerability in an unnamed file-sharing system during a span from October 2025 to mid-July 2026.
This breach has revealed sensitive information such as Social Security numbers, as well as personal details including names, birth dates, gender, race, and various military service records. The alert specifies that the personnel files were not encrypted.
Reports from CNN and Federal News Network suggest that an official from the Pentagon mentioned the breach affects approximately 2.8 million living individuals and nearly 300,000 deceased persons.
As of March, there are around 1.3 million active military members in the U.S.
While the DMDC may not be commonly recognized by the public, it plays a crucial role as a records-keeping entity within the Department of Defense. The DMDC manages over 60 million records pertaining to U.S. military and civilian personnel and their families, facilitating the determination of benefits and entitlements, including healthcare and retirement. This unit functions as the military’s primary identity management authority, linking personnel to credentials such as smart cards and passwords necessary for accessing Pentagon facilities and systems.
“Our mission is to ensure that authorized individuals have the correct access while preventing unauthorized access, making the security of identity information essential,” states the DMDC’s website.
The Department of Defense, which oversees the DMDC, has indicated that there’s no evidence currently suggesting that the stolen information has been misused, although the reasoning behind this conclusion remains unspecified. Efforts to reach a Pentagon representative for details regarding any communication with the attackers—whose identities remain unknown—went unanswered.
This incident is the latest significant breach of federal employees’ personal data, following a breach at the FBI in September attributed to the ShinyHunters hacking group. They claimed to have accessed personal information related to most of the FBI’s agents and employees, including applicants. This breach has been labeled a “counterintelligence disaster” due to the potential risk of foreign entities using the information for espionage against federal personnel.
The ShinyHunters group has stated they will refrain from publicly releasing the stolen data related to the FBI.
Both the recent incidents involving the FBI and the DMDC reflect previous cases of government personnel record theft. One notable example occurred in 2015 when a breach of the U.S. government’s Office of Personnel Management was largely linked to China, resulting in the theft of private records from over 22 million government employees, many of whom held security clearances.
If you have received a notification about this data breach, we’re interested in hearing from you. You can securely contact the reporter via Signal or email.
Purchases made through links in our articles may earn us a small commission, without affecting our editorial independence.