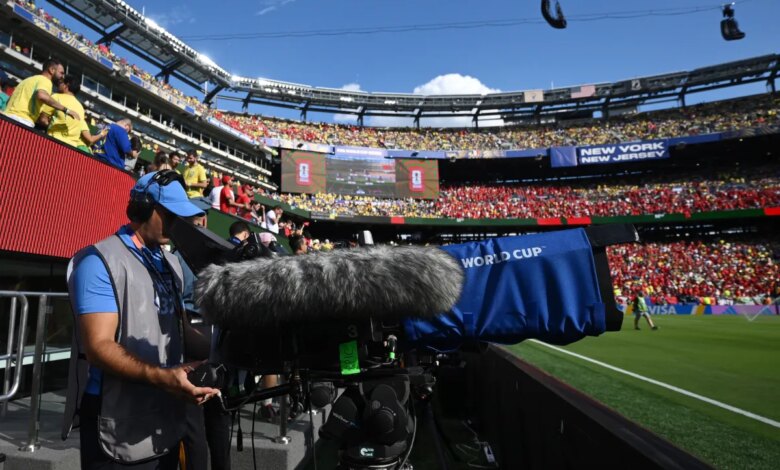
A cybersecurity expert has revealed that she exploited a basic security vulnerability to gain access to FIFA’s internal systems, granting her complete control over the live broadcasts of World Cup matches.
The expert, known as BobDaHacker, explained that she merely signed up as a player agent on FIFA’s official registration site. This, coupled with a flaw in FIFA’s backend API—which failed to verify user authorization—enabled her to unlock numerous internal FIFA platforms.
Among the systems she accessed were those that permit broadcasters to manage on-screen content seen by viewers around the world, as well as the information displayed to commentators during matches, according to her findings.
“An individual with malicious intent could potentially take control of every camera at once. Someone could have even played a prank during the FIFA World Cup,” BobDaHacker noted in a blog entry published Tuesday.
After reporting the vulnerability late Tuesday evening in Japan, BobDaHacker noted that FIFA rectified the issue within a few hours, yet did not acknowledge her report.
FIFA has not responded to inquiries for comment regarding this incident.