A series of cyberattacks targeting water utilities across the United States since late last month has raised significant concerns nationwide.
For years, hackers, whether affiliated with governments or acting independently, have set their sights on water utilities and other critical infrastructure, particularly in the energy sector. The recent attacks, reportedly linked to Iranian operatives, are particularly alarming due to their extensive reach, affecting facilities in about twelve states.
The U.S. is home to over 150,000 water systems, many managed by local entities. While this fragmentation could complicate coordinated attacks, it also means that these smaller operators often lack the necessary resources or cybersecurity measures to defend against such threats.
Cybersecurity experts have historically observed that Iranian hackers tend to engage in opportunistic attacks on less-secure targets. This recent wave, however, suggests a notable escalation in their tactics.
In light of the developments over the past two weeks since the initial reports of these attacks, it seems prudent to summarize what has been revealed and what remains uncertain.
Locations of the Attacks
On July 28, authorities in Minnesota disclosed that more than 30 communities faced coordinated cyberattacks on their water treatment facilities.
Just two days later, the FBI confirmed that water and wastewater utilities in several states reported similar issues, with some facilities experiencing impacted operations. In addition to Minnesota, facilities in Arkansas, Georgia, New Jersey, and Michigan have also been targeted.
Suspected Perpetrators
While it is not yet definitively known who is responsible for the attacks, initial suspicions point towards the Iranian government.
As of this moment, the U.S. government has not publicly identified any suspects for these coordinated attacks.
The first incidents in Minnesota occurred shortly after a warning from the U.S. Cybersecurity and Infrastructure Security Agency (CISA) about Iranian hackers targeting internet-connected components in water systems and the energy sector, although specific locations of these attacks were not disclosed. This initial warning was first issued in April and later updated before the events in Minnesota.
Following the Minnesota incidents, former President Trump suggested that the matter was mismanaged at the state level rather than a product of Iranian aggression, possibly in relation to Minnesota’s democratic leadership.
This claim came a day after a report highlighted that the Water Information Sharing and Analysis Center, a nonprofit that shares cybersecurity information with water sector entities, suggested the attacks mirrored those mentioned in CISA’s alert, implying Iranian involvement.
Recent reports now indicate that U.S. intelligence agencies believe that Iran, specifically the Islamic Revolutionary Guard Corps (IRGC), may be behind these hacks. The specific unit responsible remains unclear, and authorities may be hesitant to contradict Trump’s public statements.
Iranian cyber operatives have previously targeted critical infrastructure in the U.S., and these latest attacks might represent a method of retaliating amid ongoing tensions.
Historically, Iranian hackers have had limited success with cyberattacks in the U.S. Notably, a group known as Handala disrupted the operations of the medical technology company Stryker last March. The U.S. government has linked this group to Iran’s Ministry of Intelligence and Security.
Consequences of the Attacks
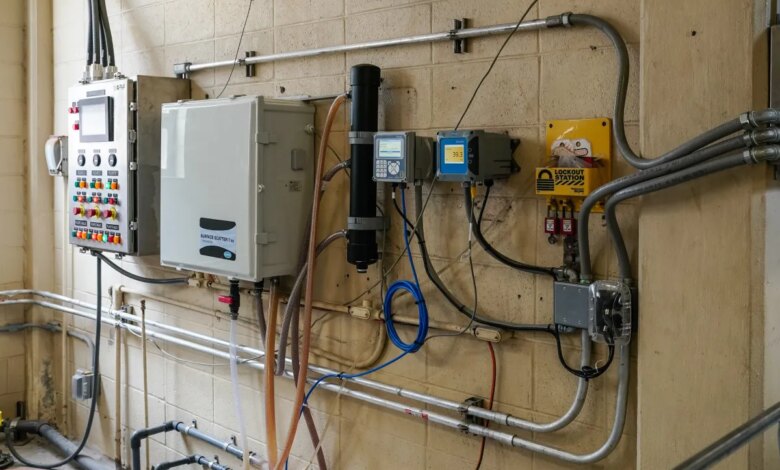
Many systems within critical infrastructure are accessible on the internet and can be relatively easy to exploit. A recent report from cybersecurity firm Forescout indicated that over 2,800 controllers in U.S. water systems were online and vulnerable. While not all exposed systems lead directly to control breaches, there have been cases of significant impact during recent attacks.
The FBI stated that some cyberattacks led to pressure loss in water systems, which could allow untreated groundwater to enter the plumbing, raising alarms about potential flooding. For example, the town of Braham in Minnesota temporarily shut down its water plant, advising its residents to conserve water. Maple Plain, also in Minnesota, enacted a brief state of emergency, while officials in a Georgia county urged residents to boil their water as a precaution.
Perhaps the most profound impact of these attacks is psychological. Extensive media coverage has fueled public anxiety over the safety of essential resources like water, which may align with the hackers’ goal of instilling fear and panic.